What a Darknet IP Address Actually Is
A darknet IP address is not a single thing. When you visit a .onion site, you are not connecting to an IP address in the traditional sense. Instead, Tor creates an encrypted circuit through multiple volunteer-run relays, and the final relay (the exit node) makes the request to the destination. The destination server sees the exit relay's IP, not yours. Onion services themselves do not have public IP addresses. They are hidden services that exist only within the Tor network, identified by their .onion address (a 56-character v3 address or 16-character v2 address, now deprecated). The .onion address is a cryptographic hash of the service's public key, not an IP. This design means that even if someone intercepts traffic, they cannot easily map the .onion address to a physical location or ISP.
How Tor Routing Masks Your Real IP
Tor works by routing your traffic through at least three relays before it reaches its destination. Your computer connects to an entry guard relay, which connects to a middle relay, which connects to an exit relay. Each relay only knows the IP of the relay before and after it in the chain. The exit relay sees the destination server, but the destination does not see your IP. Instead, it sees the exit relay's IP. This is called onion routing. The encryption is layered: each relay decrypts one layer of encryption, revealing only the address of the next relay. A fundamental property documented by the Tor Project is that no single relay can see both your IP and the destination you are visiting. This separation is what makes Tor's anonymity model work. However, if an attacker controls both your entry relay and the exit relay, they can correlate traffic patterns and potentially link your IP to your destination. This is why the Tor Project recommends using bridges if your ISP or network administrator monitors Tor usage.
The Difference Between Exit Relays and Hidden Services
Exit relays are volunteer-operated nodes that make requests to the regular internet on behalf of Tor users. They have public IP addresses and are listed in the Tor directory. When you browse a regular website through Tor, the exit relay's IP is what the website logs. Hidden services (onion services) work differently. They do not use exit relays. Instead, they connect to the Tor network directly and advertise their presence through introduction points, which are other Tor relays. When you connect to a hidden service, your traffic never leaves the Tor network. The service operator never learns your IP address, and you never learn the service's IP address. Both of you are identified only by your .onion addresses. This is why hidden services are considered more private than using Tor to browse the regular web. The trade-off is that hidden services are slower because all traffic stays within Tor's volunteer network.
Why Darknet Address Anonymity Matters in Practice
Anonymity on the darknet protects journalists, activists, and ordinary people in countries with censorship or surveillance. It also protects whistleblowers who need to leak documents without revealing their identity or location. SecureDrop, a platform used by news organizations to receive anonymous tips, operates as a hidden service. This means sources can submit information without their ISP, government, or the news organization itself knowing their IP address. The same technology is used by political dissidents, privacy advocates, and people seeking information that is blocked in their country. However, anonymity also enables criminal activity. Darknet markets have used hidden services to hide their infrastructure from law enforcement. The anonymity is not absolute: law enforcement has successfully identified and prosecuted darknet market operators by combining traffic analysis, operational security mistakes, and traditional investigative work. The Tor Project documentation emphasizes that Tor provides anonymity against network surveillance, not against all forms of attack. If you reveal your identity through your behavior or by using the same username across platforms, Tor cannot protect you.
Common Misconceptions About Darknet IP Tracking
A widespread myth is that your IP address is hidden the moment you open Tor Browser. In reality, your IP is visible to your ISP and any network observer until your traffic enters the Tor network. Your ISP can see that you are using Tor, even if they cannot see what you are doing inside Tor. Some people believe that using Tor makes you invisible to law enforcement. This is false. Law enforcement has successfully de-anonymized Tor users through a combination of technical analysis, metadata, and operational security failures. Another misconception is that all .onion sites are equally anonymous. Some are run by law enforcement as honeypots. Others are phishing clones designed to steal credentials. The anonymity of the technology does not guarantee the trustworthiness of any individual service. A third myth is that a VPN plus Tor provides better anonymity than Tor alone. Using a VPN before Tor can actually weaken your anonymity by concentrating your traffic through a single provider. The Tor Project recommends using Tor directly, or using Tor Browser's built-in bridge feature if your network blocks Tor.
Reality Check: What Law Enforcement Knows
Law enforcement agencies have successfully prosecuted darknet market operators, vendors, and users. According to court records and public law-enforcement press releases, these prosecutions have relied on a combination of techniques: traffic analysis at ISP level, blockchain analysis for cryptocurrency transactions, operational security mistakes by suspects, and cooperation from service providers. The FBI and other agencies have run Tor exit relays and hidden services as part of investigations, allowing them to observe traffic patterns. This matters because it shows that using the darknet does not grant immunity from investigation. A person who uses the same username across darknet markets and clearnet platforms, or who makes a mistake in operational security, can be identified. The Silk Road case is a historical example: the operator was identified through a combination of forum posts, Bitcoin analysis, and traditional detective work, not through breaking Tor itself. Modern law enforcement has become more sophisticated in analyzing onion service traffic, though the Tor network itself remains resistant to large-scale de-anonymization attacks. For ordinary users, the practical lesson is that anonymity is a tool, not a guarantee, and it requires consistent operational security.
Verifying Onion Addresses and Avoiding Phishing
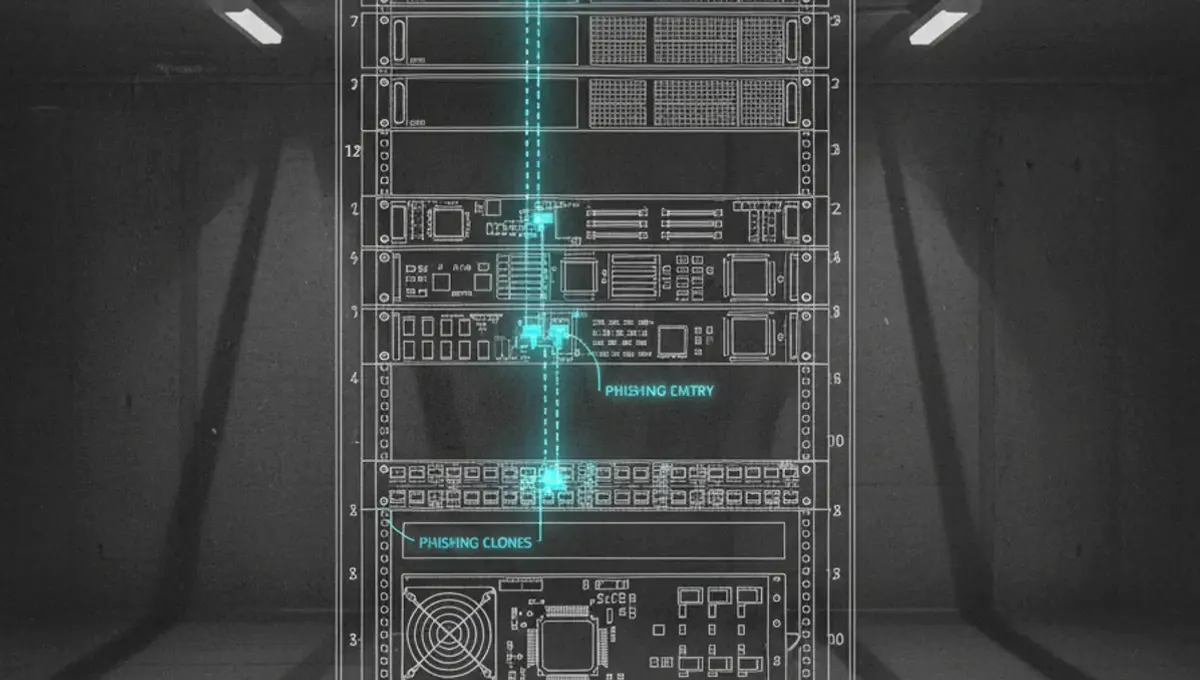
Because .onion addresses are long, random-looking strings, they are difficult to remember and easy to spoof. Phishing clones of popular darknet sites are common. A phishing clone is a fake site that looks identical to a legitimate one but is run by an attacker. When you type the wrong address or click a malicious link, you land on the clone and enter your credentials, which the attacker captures. To verify a legitimate .onion address, look for PGP-signed announcements from the service operator. The operator's public key should be published on their official clearnet site or in a trusted directory. You can verify the signature using GnuPG to confirm that the address has not been tampered with. Never rely on a .onion address found in a forum post or a Reddit thread without verification. The best darknet site operators publish their addresses on their own websites and sign them with PGP. If a site claims to be the best darknet website but does not publish a PGP-signed address, treat it with suspicion. Bookmarking the correct address after verification is safer than searching for it each time. Tor Browser also warns you if you visit a site with an invalid SSL certificate, which is another sign of a phishing clone.
Taking Control of Your Darknet Privacy
If you decide to access the darknet, start by downloading Tor Browser from the official Tor Project website only. Verify the signature of the download using the provided GPG key. Open Tor Browser and allow it to connect to the Tor network. Do not maximize your browser window, as this can make you easier to fingerprint. Do not enable plugins or extensions unless you understand the security implications. When visiting any site, assume it could be a phishing clone. Verify addresses through PGP-signed announcements before entering sensitive information. Use a dedicated device or virtual machine if you are accessing sensitive services. Never use the same username across multiple sites. Do not assume that using Tor makes you safe from malware or social engineering. The technology protects your IP address and location, but it does not protect you from your own mistakes. If you are concerned that your email or personal information has been exposed on the darknet, visit the Useful Resources page of this site for guidance on monitoring and verification tools.
Common Questions
Can someone find my real IP address if I use Tor
No, if you use Tor correctly. Tor routes your traffic through multiple relays, and the destination server sees only the exit relay's IP, not yours. However, if your ISP or network observer monitors your connection, they can see that you are using Tor. Your ISP cannot see what you are doing inside Tor, but they can see that you are using it.
What is the difference between a darknet IP and an onion address
A darknet IP address typically refers to the exit relay's IP that a destination server sees when you visit a site through Tor. An onion address is a .onion domain name that identifies a hidden service within the Tor network. Hidden services do not have traditional IP addresses; they are identified by their cryptographic .onion address.
How do I know if a darknet address is real or a phishing clone
Look for a PGP-signed announcement of the address from the official operator. Verify the signature using GnuPG and the operator's public key. If the site does not publish a PGP-signed address, treat it with suspicion. Never rely on addresses found in forum posts or Reddit threads without independent verification.
Can law enforcement trace me on the darknet
Law enforcement cannot easily break Tor itself, but they can identify users through operational security mistakes, traffic analysis, metadata, and traditional investigative work. Court records show that darknet market operators have been successfully prosecuted. Using Tor does not grant immunity from investigation if you make mistakes or reveal your identity.
Is using a VPN before Tor better for privacy
No. Using a VPN before Tor can actually weaken your anonymity by concentrating your traffic through a single provider. The Tor Project recommends using Tor directly. If your network blocks Tor, use Tor Browser's built-in bridge feature instead of a VPN.